Understand SOC Processes and Best Practices
How do Security Operations Centers (SOCs) operate, their key SOC process, their best practices, and much more?


How do Security Operations Centers (SOCs) operate, their key SOC process, their best practices, and much more?
Dealing with cyber threats means confronting hostile actors who are looking to infiltrate and compromise your data and systems. They may try to steal your credentials or use social engineering techniques to gain access, and if they succeed, they may steal sensitive data. Furthermore, you may unintentionally leave your IT systems vulnerable due to improper configuration, a lack of protection, or unmanaged vulnerabilities. With so many potential threats, how do you build a strong cyber defense? A security operations center (SOC) could be one possible solution.
In this article, we’ll explore security operations centers, how they operate, their key processes, best practices, and much more.
What Is a Security Operations Center?
A security operations center is a centralized team within an organization dedicated to continuously monitoring, detecting, preventing, and responding to cybersecurity threats. A SOC framework is the documented model of people, processes, and technology that governs how a SOC detects, investigates, and responds to threats. The SOC plays an important role in maintaining an organization’s IT defenses by tracking potential attack surfaces across systems, networks, and personnel. It makes sure that security tools are well-maintained and kept up to date to stay ahead of new cyber threats and industry changes.
SOC Operations
The operations of a security operations center can change based on what the organization aims to achieve. Some SOCs help people within the organization by protecting its own systems. Others operate as part of a managed security service provider (MSSP), offering SOC services to external clients.
The SOC Team Structure
A SOC is more than just one analyst staring at a monitor. It’s a structured team with distinct roles and responsibilities. The typical hierarchy includes the following:
- L1 SOC analysts who monitor alerts and conduct initial investigations
- L2 analysts who conduct detailed analysis and escalate confirmed threats
- L3 analysts who perform advanced threat detection , response, and forensic analysis
- A SOC manager who is responsible for efficient operations across the entire SOC
SOC analysts also frequently communicate with other teams, such as incident response (IR) teams, threat intelligence teams, and IT departments, when handling security incidents.
Tools Used in a SOC
A SOC uses tools to monitor, detect, and respond to security threats effectively. A security information and event management (SIEM) system is an important technology that acts as a central hub for gathering and examining security logs from various sources. A SIEM helps analysts spot suspicious activity in real time by gathering data from firewalls, servers, endpoints, and other network devices.
SOCs use log collection agents and methods alongside SIEM to make sure they have a complete view of the IT environment. These tools collect security data from endpoints, cloud services, and network infrastructure, helping analysts piece together events and spot potential threats more easily.
SOCs use various tools to handle threats, such as firewalls, endpoint detection and response (EDR) solutions, and threat intelligence platforms. These tools help stop harmful activities, manage security issues, and offer automated solutions when needed. Using these technologies, a SOC can make threat detection, investigation, and response easier, helping to improve an organization’s cybersecurity efforts.
SOC vs SIEM
A SOC is the team and processes that defend an organization, while a SIEM is one of the technologies that team operates. The SOC brings the analysts, workflows, and decision-making, and the SIEM supplies the centralized data and correlation those analysts rely on to spot and investigate threats.
Adapting to Different SOC Models
Although the basic structure is similar, SOC operations can differ from one organization to another. Some organizations might refer to all analysts as SOC analysts instead of classifying them as L1, L2, or L3. The way reports are handled and how responses are managed can change depending on whether the security operations center is inside a company or part of a managed security service provider (MSSP).
Knowing these parts of a SOC is important for working well in any security setting. As SOC analysts gain experience, they better understand these aspects, helping them handle the challenges of security operations more easily.
SOC Processes
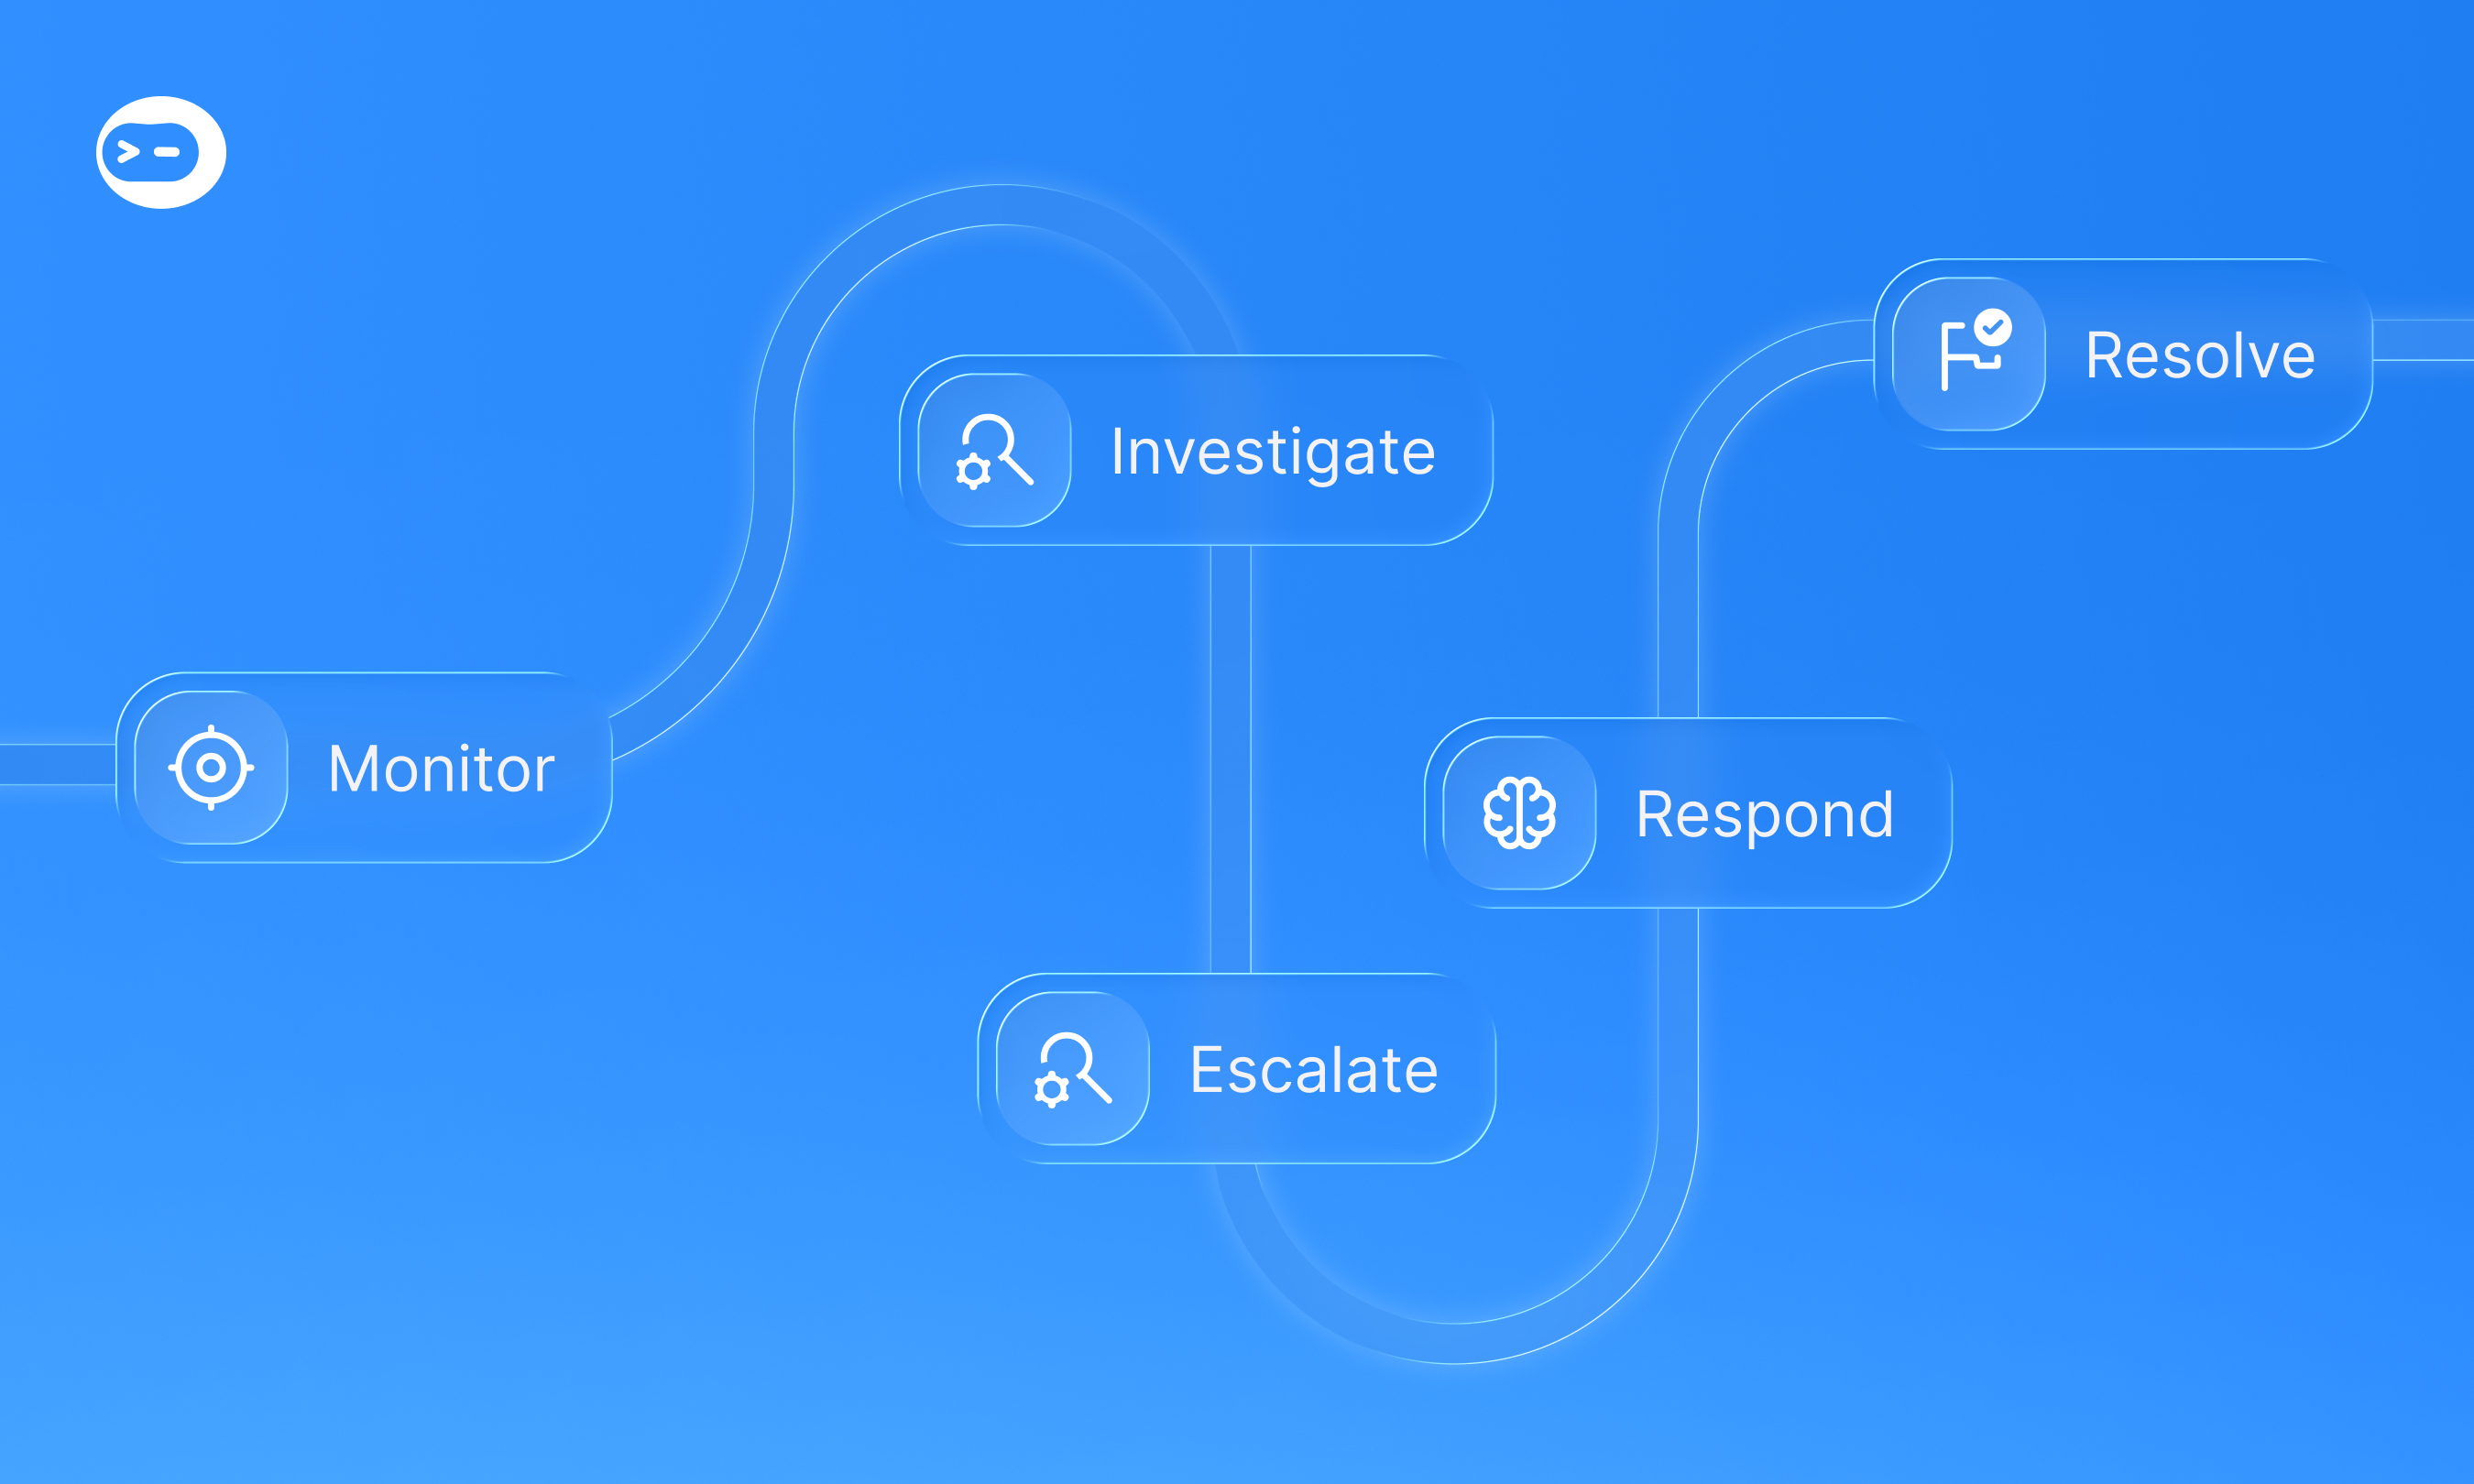
A SOC has clear processes that’ll help you find, stop, notice, react to, and bounce back from security threats.
- Continuous threat monitoring: This step involves analyzing alerts from security tools, such as SIEM systems, to identify potential threats. This includes detecting attacks such as SQL injections, network scans, and unauthorized access attempts. The SOC operates around the clock, actively monitoring incoming alerts for potential threats.
- Investigation and escalation: When an alert is triggered, it’s investigated to make sure it’s legitimate. If the alert is deemed malicious, it’s forwarded to Level 2 or Level 3 analysts for further investigation. The escalation process varies by organization; it may be done via email or a specialized security tool.
- Contextual information gathering: When conducting an investigation, it’s important to consider not only the immediate security event but also the preceding and subsequent events. Furthermore, external threat intelligence sources can provide useful context when determining the significance of an event.
- Incident declaration and reporting: After confirming an incident, determine who has the authority to declare it officially. This responsibility may fall to L3 analysts or require managerial approval. Following declaration, reports must be generated and shared in accordance with organizational policies, whether immediately or through periodic summaries (for example, monthly reports).
- Asset discovery: Finding and listing IT assets is an important part of SOC processes. Knowing an organization’s setup helps find weaknesses and secure important systems.
Understanding these fundamental SOC processes allows security professionals to better prepare for the real-world challenges they’ll face in an operational SOC environment.
SOC Challenges
One of the most difficult challenges when putting together or outsourcing a SOC is its high cost. Managing a twenty-four-hour security team requires skilled professionals, a secure facility, and advanced security tools.
Another major problem is the lack of skilled workers. SOC operations depend on skilled security analysts to find, investigate, and deal with threats as they happen, and as cybersecurity experts are in high demand, it’s hard for companies to find and keep the skilled workers they need to run their SOC effectively. The 2026 SANS/GIAC Cybersecurity Workforce Research Report found that 27% of organizations experienced security breaches as a direct result of workforce capability gaps. It also found that 60% of organizations now identify skills quality, not headcount, as their top workforce problem.
In addition to staffing issues, the integration and interoperability of security tools presents significant technical challenges. A SOC typically relies on multiple security solutions, and making sure these tools work together seamlessly requires manual effort and specialized expertise, which frequently leads to inefficiencies.
When an incident occurs, the complexity of the investigation and slow response times can impede a SOC’s effectiveness. To understand the full scope of an attack, analysts must combine data from various sources, which can be time-consuming. As a result, threat detection and response may be delayed, allowing threats to stay in corporate systems longer than necessary.
In addition to these basic challenges, SOCs deal with alert overload as analysts are bombarded with a huge number of security alerts every day. This can lead to alert fatigue, where important threats are missed because there are too many notifications. Similarly, not having clear visibility between network and endpoint security tools makes it difficult to understand the complete picture of potential threats.
Automating processes, using tools better, and planning wisely can reduce risks for organizations despite these challenges. By addressing these issues, businesses can improve their SOC’s cyber threat detection and response.
SOC Best Practices
Strategic planning, the right tools, and well-defined processes are needed to build an effective SOC. The following best practices can help your organization succeed whether you’re establishing an in-house team or working with an external SOC.
Define the SOC’s Objectives and Responsibilities
The foundation of any SOC begins with a clear understanding of its purpose. Organizations need to specify the threats that the SOC will watch for, explain how they will handle incidents, and clarify how the SOC fits into the overall cybersecurity plan. Clear goals help the team to be well-prepared and trained to tackle the security issues they will likely face.
Build a Skilled and Well-Rounded Team
A strong SOC needs both technical and non-technical skills. Security analysts, incident responders, and network administrators provide essential technical support for the team. Meanwhile, project managers and communication specialists connect security efforts with business activities. Because there is a lack of cybersecurity experts, organizations might require resources to train their existing staff.
Invest in the Right Security Tools
SOC teams use a variety of security technologies, including SIEM systems, intrusion detection and prevention tools, and vulnerability management solutions . However, simply adding more tools is not always the solution. Instead, organizations should focus on integrating tools that meet their specific security requirements and fully training the team to use them effectively.
Establish Standard Operating Procedures
Consistency is critical to effective security operations. Well-documented procedures for detecting, responding to, and reporting incidents give SOC analysts a clear path to follow. These processes should be reviewed on a regular basis to keep up with evolving threats and make sure the team can respond quickly and effectively when an incident occurs.
Test and Improve SOC Operations Continuously
A SOC is not a “set it and forget it” solution; continuous improvement is required. Use regular security drills, attack simulations, and team training so that SOC personnel are ready to deal with new and emerging threats. Organizations should also update their tools and workflows as the cybersecurity landscape changes.
Foster Collaboration Across Teams
SOC teams don’t operate in isolation. Effective security operations require coordination with IT, compliance, and executive leadership. Establishing clear communication channels and a well-defined incident management plan ensures that security incidents are addressed efficiently and that security priorities align with broader business objectives.
Modernizing the SOC with AI and Automation
An AI SOC, also called an agentic SOC, is an operating model where AI agents run alert triage, enrichment, investigation, and response, with security analysts reviewing and approving actions. The model shifts routine, high-volume work to agents so analysts can focus on judgment calls and complex threats. Instead of only summarizing alerts, agents carry an investigation from raw signal to a documented, review-ready case.
Teams reach this model by automating SOC workflows that pair deterministic workflows with reasoning-based micro-agents. Deterministic steps handle predictable tasks reliably, while micro-agents reason across evidence to investigate cases that rigid playbooks cannot. On Blink, both run inside a platform-enforced harness the agent cannot see, negotiate, or reason around, so every action stays within the bounds the security team sets.
Control comes from more than the harness. Human-in-the-loop decisions keep analysts in charge of when the machine stops and the human starts. Full auditability records the reasoning, evidence sources, and actions behind every case, giving teams a defensible trail for compliance and post-incident review.
This approach is a force multiplier for the team you already have, not a replacement for it. Agents absorb repetitive triage and enrichment, and analysts apply their expertise where it matters most. The direction of travel is clear: the 2026 SANS AI Survey found that AI use across cybersecurity functions jumped from 50% to 78% in a single year.
Conclusion
Building a SOC is a complex but necessary investment in an organization’s security posture. By clearly defining objectives, assembling the right team, leveraging the best tools , and continuously improving processes, businesses can create a SOC that not only detects and mitigates threats but also strengthens overall cybersecurity resilience.
Modernize Your SOC With Blink
Modernizing your SOC means moving from manual triage to agents that investigate and respond under your team’s control. Blink’s AI SOC runs the full investigation and response cycle with human-in-the-loop approval and full auditability across your existing stack. Request a demo to see how it fits your security operations.
Frequently Asked Questions
What Is A Security Operations Center (SOC)?
A security operations center (SOC) is a centralized team dedicated to continuously monitoring, detecting, preventing, and responding to cybersecurity threats. It tracks potential attack surfaces across an organization’s systems, networks, and personnel. It also keeps security tools maintained and up to date so the team can stay ahead of new threats.
What Is A SOC Framework?
A SOC framework is the documented model of people, processes, and technology that governs how a SOC detects, investigates, and responds to threats. It defines the team’s roles, standard operating procedures, and the tools that support detection and response. A clear framework helps the team respond consistently as threats evolve.
What Is The Difference Between A SOC And A SIEM?
A SOC is the team and processes that defend an organization, while a SIEM is one of the technologies that team operates. The SIEM centralizes and correlates security logs so analysts can spot suspicious activity in real time. The SOC provides the people and workflows that investigate and respond to what the SIEM surfaces.


Related: