Agentic GitHub Repository Access Reviews: Why Manual Collaborator Management Breaks at Scale
A GitHub repository access review checks who can reach your repositories, teams, and organizations, then decides whether that access should continue. Adding and removing collaborators by hand works for one repository, but it breaks across an organization. Continuous, governed, automated reviews are how security teams hold least privilege.

How Do You Add and Manage Collaborators in GitHub? (The Manual Baseline)
These mechanics are where most teams start. They are correct and useful, and they are also the baseline that stops scaling once you manage many repositories and identities.
What Permission Levels Can a GitHub Collaborator Have?
GitHub grants access at role granularity, so pick the lowest role that lets the person do their job.
- Read: view and clone the repository; suitable for stakeholders and reviewers.
- Triage: manage issues and pull requests without write access to code.
- Write: push to the repository and manage most content.
- Maintain: manage the repository without access to sensitive or destructive actions.
- Admin: full control, including settings, access, and deletion.
To grant a permission, your own role must be equal to or higher than the level you assign. Default to Read, and escalate only when a task requires it. That is least privilege applied at the point of grant.
How Do You Add a Collaborator Using the GitHub UI?
For a single repository, the console path is short:
- Open the repository, then go to Settings.
- In the sidebar, select Collaborators and teams.
- Under Manage access, choose Add people.
- Search for the username, full name, or email, then select the account.
- Set the permission level, then send the invitation.
The collaborator gets an email invitation and appears once they accept. Enterprise organizations can also apply an outside-collaborator policy that restricts who can be invited, which is worth enforcing before access sprawls.
How Do You Add a Collaborator Using the GitHub API or CLI?
For repeatable and scripted access, use the REST endpoint that adds a collaborator:
PUT /repos/{owner}/{repo}/collaborators/{username}
GitHub CLI:
gh api \
  --method PUT \
  -H "Accept: application/vnd.github+json" \
  /repos/OWNER/REPO/collaborators/USERNAME \
  -f permission='push'
Octokit.js:
await octokit.request("PUT /repos/{owner}/{repo}/collaborators/{username}", {
  owner: "OWNER",
  repo: "REPO",
  username: "USERNAME",
  permission: "push",
});
cURL:
curl -L \
  -X PUT \
  -H "Accept: application/vnd.github+json" \
  -H "Authorization: Bearer YOUR-TOKEN" \
  https://api.github.com/repos/OWNER/REPO/collaborators/USERNAME \
  -d '{"permission":"push"}'
A new invitation returns HTTP 201 Created with the invitation object. Scripting grants is faster than clicking, but it also spreads standing access faster, which is exactly why reviews have to keep pace.
Why Does Manual Collaborator Management Break at Scale?
The problem is not the individual grant. It is the accumulation of grants that no one revisits. For source code, that accumulation is a direct exposure, because a stale token or forgotten collaborator is a ready-made entry point.
Here are the failure modes Tier 2 engineers see most:
- Privilege creep and standing privilege. As BlinkOps notes in its Okta automation guide, access rights pile up beyond what a role needs.
- Stale outside collaborators and orphaned access. Unrevoked leavers and vendors create deprovisioning lag, a top source of access-related audit findings.
- Secrets committed to repositories. The Verizon 2025 DBIR found the median time to remediate a leaked secret in a GitHub repository was 94 days.
- Widespread exposure. GitGuardian reported 23.8 million secrets leaked on public GitHub in 2024, with 35% of private repositories holding at least one secret.
- Persistent risk. GitHub Docs state that hardcoded secrets stay in Git history after removal, so you must rotate the credential.
Non-human identities widen the gap. The Cloud Security Alliance reports that non-human identities outnumber humans by an enterprise average near 45 to 1. The same CSA whitepaper notes that governance of these identities rarely matches the rigor applied to humans.
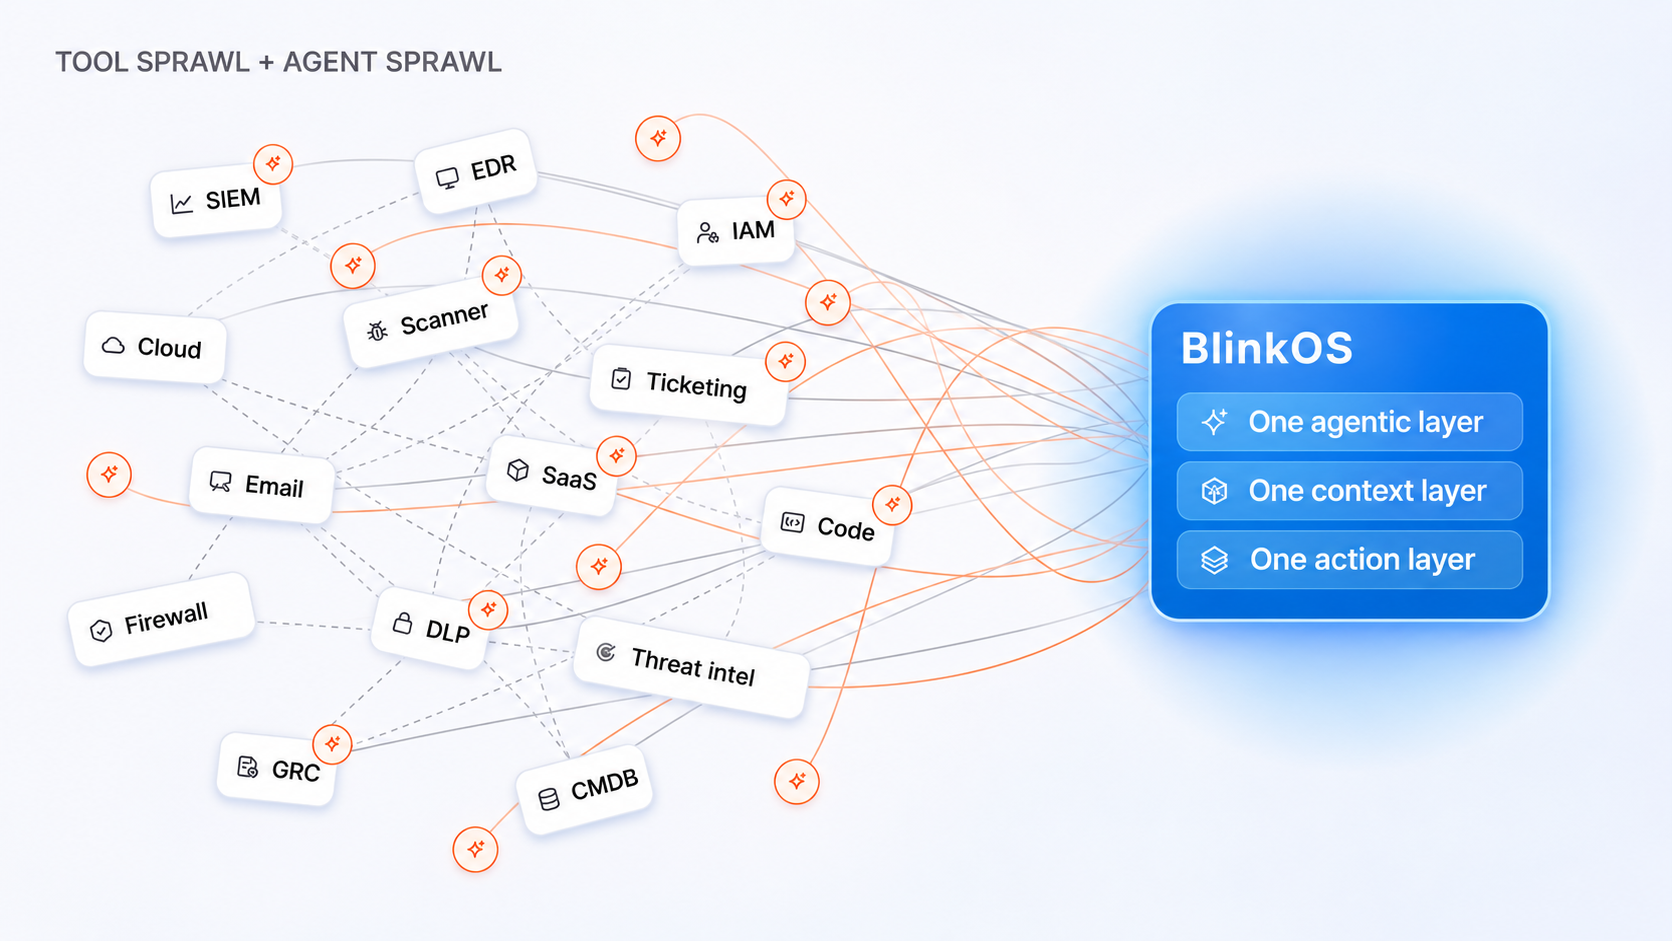
That maps directly onto GitHub. Tokens, Apps, bots, and service accounts get provisioned once and seldom reviewed. Humans are no longer the majority of your identities, yet most review processes still assume they are.
Manual reviews also drift into ritual. Ticket-driven certifications become quarterly fire drills, and fatigued reviewers approve in bulk rather than judge each grant. That is how least privilege quietly erodes between audits.
What Do Compliance Frameworks Require for GitHub Repository Access Reviews?
Auditors expect access reviews to be periodic, documented, and tied to real lifecycle events. The specifics are prescriptive.
- NIST SP 800-53 Rev. 5 control AC-2 requires full account lifecycle management, periodic membership review, and alignment with HR termination processes.
- The PCI Security Standards Council sets PCI DSS v4.0 to disable inactive accounts within 90 days and review user access every six months.
- SOC 2, per AICPA Trust Services Criteria, and ISO/IEC 27001 Annex A 5.18 both require recurring, documented reviews of user access rights at planned intervals.
Point-in-time cleanups do not satisfy these controls, because evidence goes stale between audits. This is where Agentic GRC fits: it keeps evidence current continuously, so you can comply continuously and audit any day rather than scramble each quarter.
How Do You Review GitHub Access Across an Entire Organization?
Per-repository clicks do not scale to hundreds of repositories. Review at the org and team level, and let the API do the enumeration.
- Enumerate access with the API: list org members, teams, and repository collaborators programmatically instead of opening each repository.
- Review high-privilege roles first: Admin and Maintain grants carry the largest blast radius.
- Check direct user grants that bypass teams: these are the hardest to track and revoke.
- Review GitHub App and installation access: apps are identities too, and are often over-scoped for what they use.
- Confirm repository visibility and branch protection: public exposure and unprotected branches change who can effectively change code.
- Export results as timestamped evidence: reuse the same record for the next audit.
How Do You Automate GitHub Repository Access Reviews with Agentic IAM?
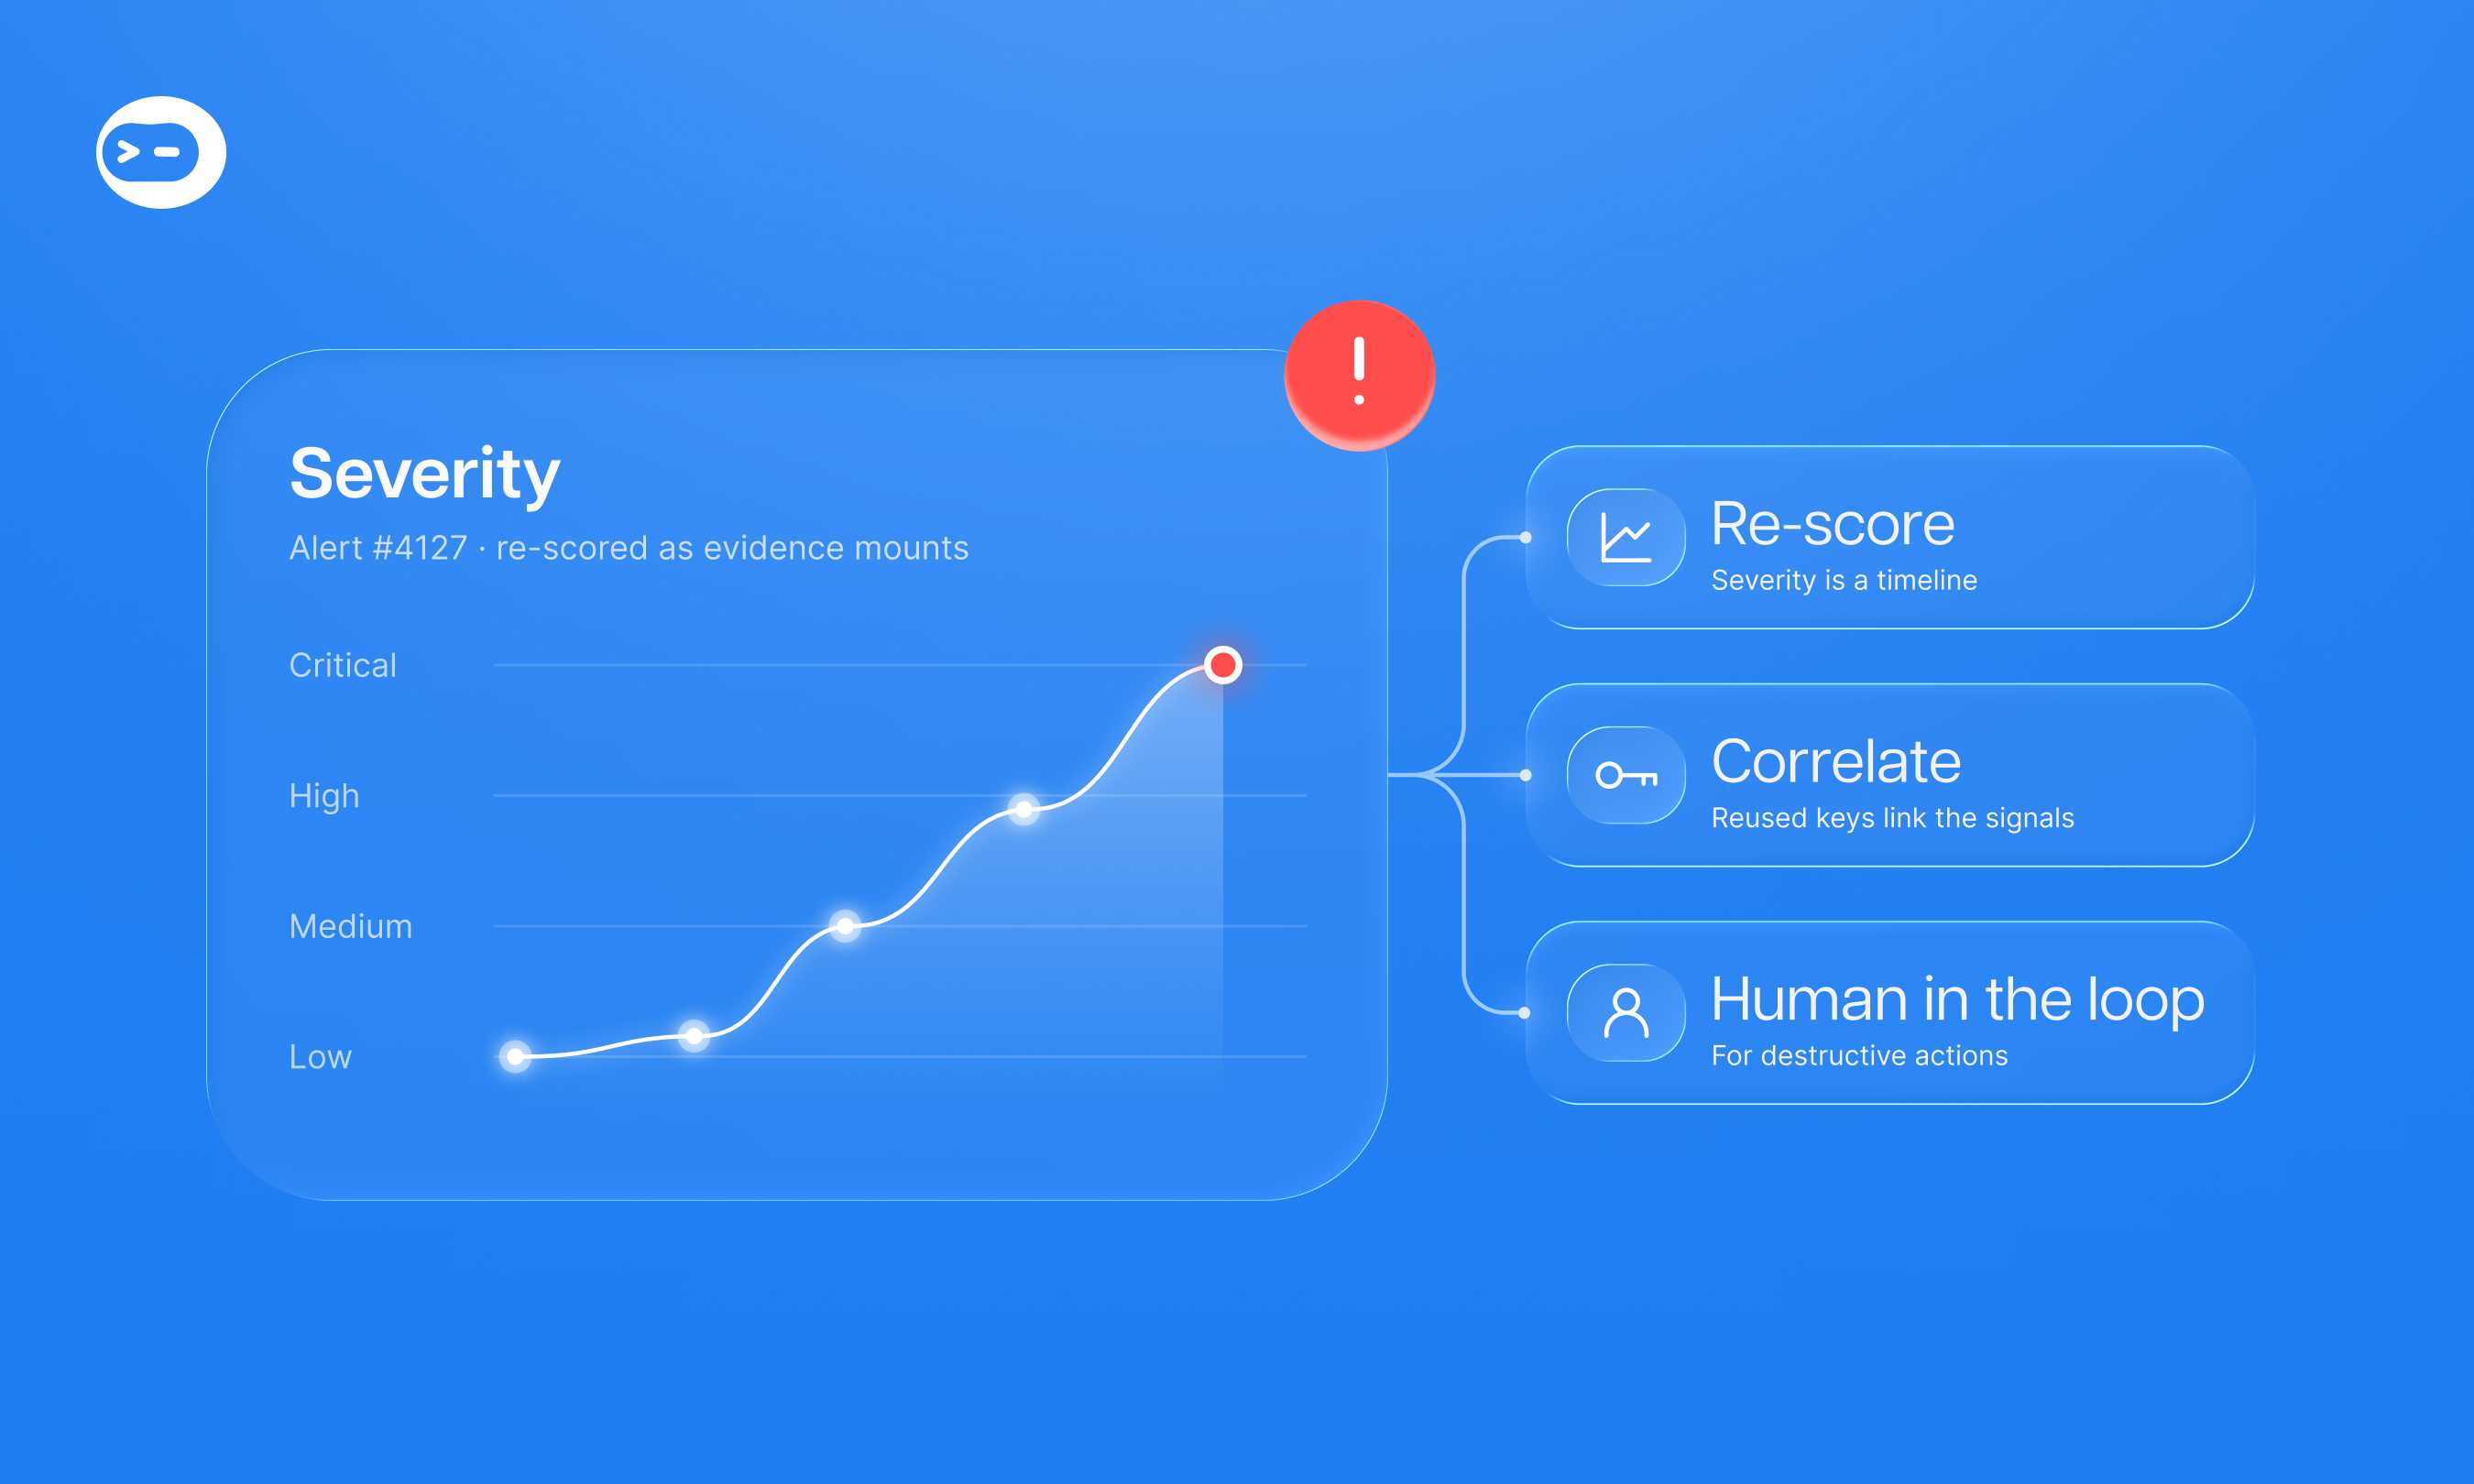
The old model grants access now and reviews it later, leaving standing privilege and quarterly rubber-stamps. The goal instead is continuous certification and just-in-time least privilege, where access is granted and revoked as needs change.
BlinkOps built Agentic IAM to agentify these processes on Blink, the Agentic Security Operations Platform, with no rip-and-replace of the identity stack you already own. Pre-built micro-agents do the work that makes manual reviews meaningless:
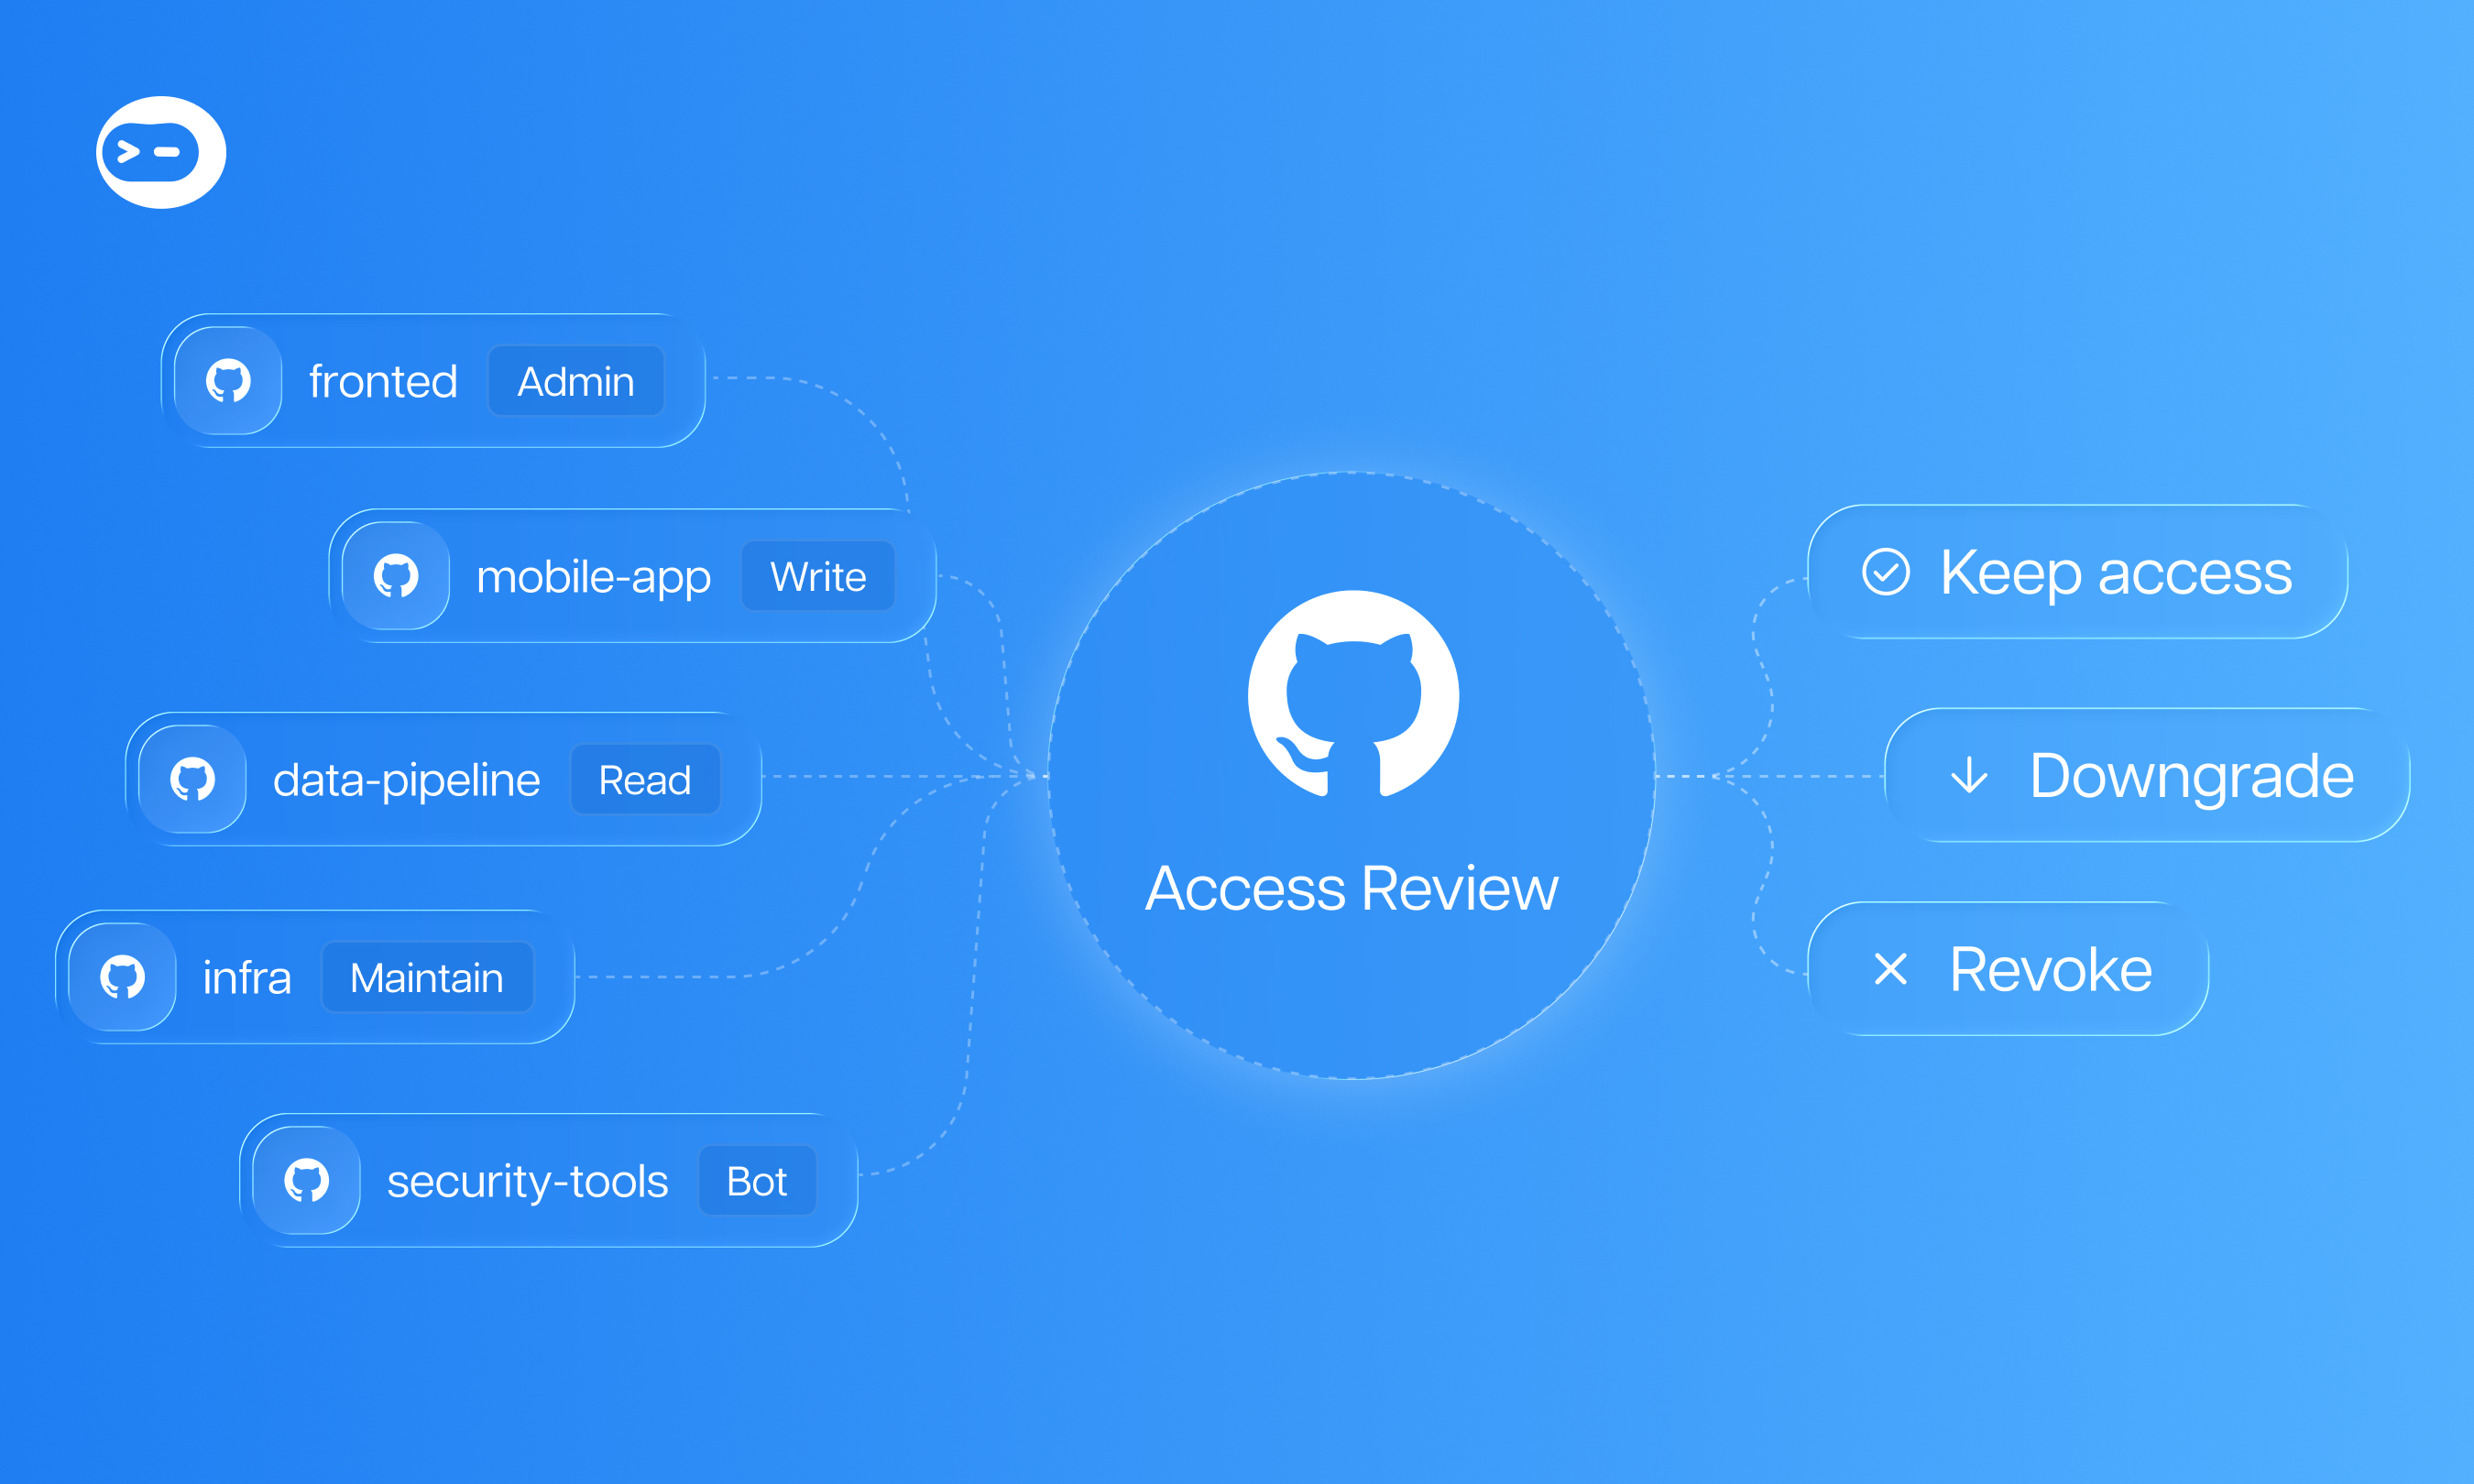
- Access Review Agent: pre-classifies each entitlement as keep, remove, or escalate, grounded in usage and peer access.
- JML Agent: revokes leaver access across systems, including GitHub, when HR marks a departure.
- Access Request Agent: evaluates each request against policy and peer access, then returns a recommendation with justification.
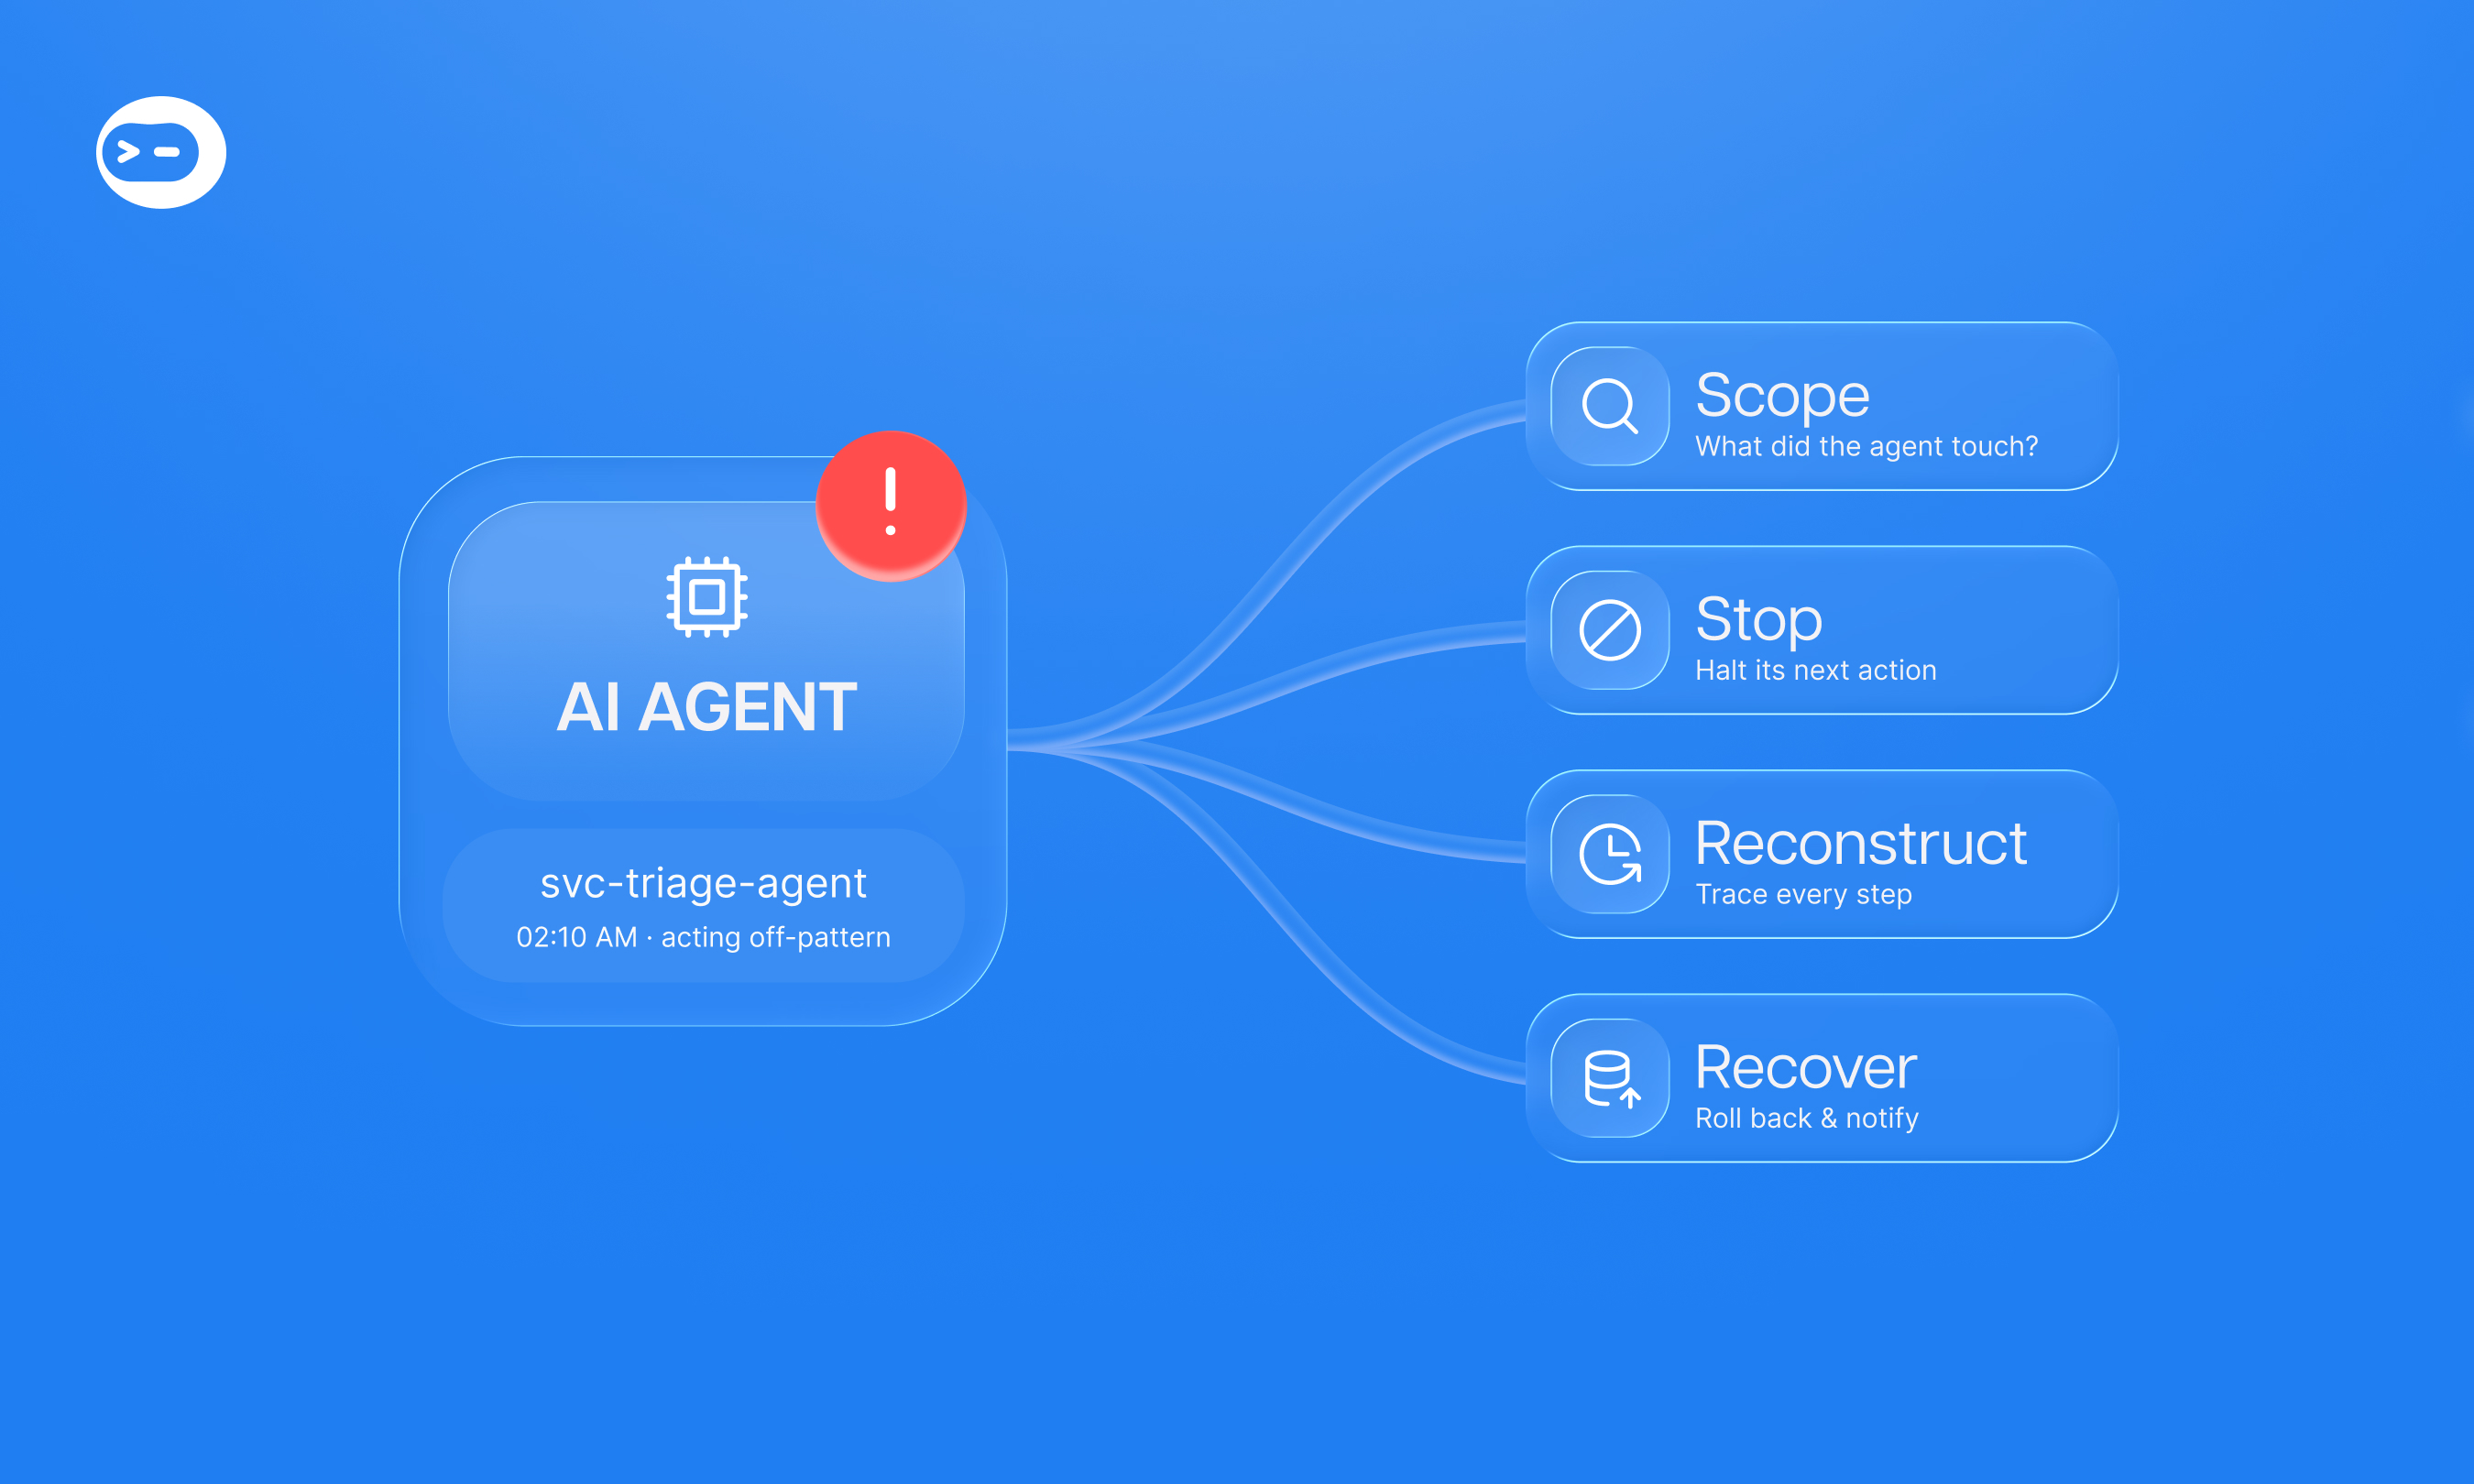
Control is the point. Reasoning agents act only through pre-approved, auditable skills inside a platform-enforced harness, a bound the agent cannot see, negotiate, or reason around. Human-in-the-loop approval governs consequential or irreversible actions, and every action is logged for audit.
This is a force multiplier for the team you already have, not a replacement for your engineers. The agents pre-classify and recommend, while your reviewers keep the final call on what matters.
It works across your identity and access stack, from GitHub and your IdP to long-tail SaaS, and it is model-agnostic. Agents learn from your team’s decisions without retraining, so reviews get sharper over time rather than more manual. When you need a GitHub-specific review flow, you can build your own agent in Agent Studio with scoped tools, permissions, and knowledge.
GitHub Repository Access Review Checklist (Practical Guidance)
Use this checklist to carry a continuous-review plan to your director:
- Inventory every human and non-human identity with access to each repository, team, and organization.
- Enforce least privilege by assigning the lowest role and managing access through teams, not one-off grants.
- Time-bound outside collaborators and vendor access, and require re-justification before renewal.
- Revoke access the same day a person leaves, driven by an HR or IdP leaver event.
- Rotate and revoke any exposed secret, since deleting the file does not invalidate the credential.
- Review access continuously instead of quarterly, and pre-classify entitlements before a human decides.
- Log every grant, change, and revocation so evidence stays audit-ready between assessments.
Move From Manual Cleanups to Continuous Governance
Manual collaborator management is a reasonable starting point and a poor operating model at scale. GitHub gives you the roles and APIs; governance keeps them honest over time. BlinkOps reports that Agentic IAM turns a typical 45-day deprovisioning cycle into a same-day, fully logged action.
Ready to see agentic access reviews on your own GitHub, IdP, and SaaS footprint? Request a demo of the Blink agentic security operations platform.
Frequently Asked Questions
What is the difference between a GitHub collaborator and an organization member?
A collaborator is granted access to a specific repository, often someone outside your organization. An organization member belongs to the org and can receive access through teams and org-level roles. Managing access by team, as covered in our IAM automation overview, scales better than per-repository grants.
How often should you review GitHub repository access?
Base cadence on your compliance obligations, then tighten from there. PCI DSS v4.0 requires review at least every six months, while SOC 2 and ISO 27001 expect recurring, documented reviews. Point-in-time reviews leave gaps between cycles, so continuous certification is the stronger control for fast-moving repositories.
How do you remove or change a collaborator’s access level?
In the UI, open Settings, then Collaborators and teams, and adjust or remove the role under Manage access. Via the API, send a PUT request to change the permission or a DELETE request to revoke it. At scale, drive these changes from lifecycle events rather than tickets, an approach our AWS IAM user walkthrough illustrates.
What is a non-human identity in GitHub and why does it matter for access reviews?
Non-human identities include personal access tokens, GitHub Apps, bots, and service accounts. Provisioned once and rarely reviewed, they accumulate standing access and risk silently. A credible GitHub repository access review must inventory and re-justify them, as our GitHub integration guide helps you connect and track.
What’s the difference between a one-time GitHub access review and continuous certification?
A one-time review is a snapshot: accurate the day it runs, stale soon after. Continuous certification evaluates access on an ongoing basis, pre-classifying entitlements and revoking on lifecycle events. It keeps least privilege intact between audits and removes the quarterly fire drill that produces rubber-stamped approvals.